cross-posted from: https://feddit.online/c/tech@feddit.online/p/2110066/a-microsoft-researcher-and-an-intern-used-ai-to-find-59-security-bugs-in-the-linux-kern
I double-dog-dare them to open the Windows codebase to outside inspection and see how many bugs that turns up.
I believe they have to do that to be used for government work.
AFAIK a lot of institutions have access to the Windows source code, including companies which are Microsoft Gold partners. Since one cannot completely exclude that the code is covertly copied, you can reasonably assume that a few bad guys with the latest AI tools are looking at the windows code base.
“My back door is only for you baby” - Microsoft probably
And how many of those are exploitable in real-world situations? Raw counts of bugs aren’t all that meaningful.
Is a bug a bug if it never occurs?
According to gpt-6.1-sol, yes it is, very much so, “alert alert warning you cannot do this!”
After working a while with this model I’m not much impressed anymore by countless potential security issues. I switched to Opus 5.5.
How can you scream… When you have no mouth?
Is this why their services are not working now?
They accidentally fixed the wrong operating system.
Windows - looks inside - 23 years old linux bug
Well, they are prioritising stability of something
deleted by creator
thanks, have your ai contact linux’s ai and i’ll go on a long fishing trip.
they’re always shoveling FUD. 365
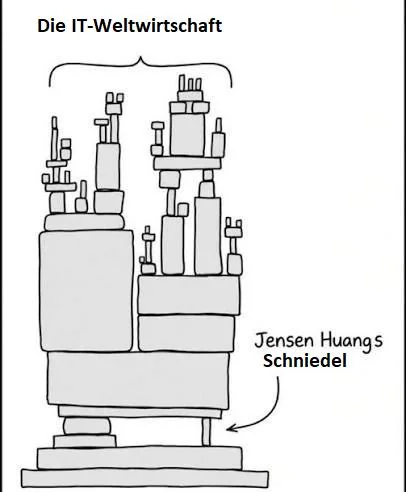
Thank you for making my system more secure, Mr. Microsoft researcher. I’ll apt upgrade right away.
and adding several hundred new ones on windows by vibe coding
Either copilot got it right or not. MS has its rep and the timing is funny.
Is that two people or one people